Profile
Security leader with more than twenty years of building, running and securing internet-scale services. I lead threat detection at Google, where my organization finds attackers across Google's infrastructure, around the clock. I set multi-year strategy, build teams that scale across continents, and make security something engineering organizations choose to adopt rather than have imposed on them.
Focus Threat detection strategy · Detection & response at planet scale · AI in security operations · Building security organizations
Selected impact
- Built Google Cloud's threat detection function and grew it 5× in three years into a follow-the-sun organization running 24/7 investigations across three continents.
- Lead threat detection for all of Google, owning strategy, detection engineering, validation and operations.
- Set Google Cloud's multi-year detection strategy and aligned VPs and GMs on its funding and reporting.
- Run detection at planet scale: thousands of rules across exabytes of logs, protecting millions of Cloud projects.
- Reported to Mozilla's board on security posture, and owned security for 100+ cloud services used by 300M+ Firefox users.
- Created widely adopted open source security tools, including SOPS (23k+ GitHub stars), and wrote Securing DevOps (Manning, 2018).
Experience
Threat Detection
2025 – nowLead Google's threat detection organization, the Detection half of Detection & Response. I'm accountable for finding attackers across Google's infrastructure, and for the strategy, people and platforms that make that possible.
- Own detection strategy end to end: threat modeling, detection engineering, validation and 24/7 operations.
- Lead a multi-team organization of managers and engineers across three continents.
- Drive the shift to AI-assisted detection and investigation, from probabilistic detection across the kill chain to model-assisted analyst workflows.
- Partner with security, Cloud and infrastructure leadership on priorities, funding and risk reporting.
Cloud Detection & Response
2020 – 2025Built and led the team that protects Google Cloud from threats across millions of projects and hundreds of thousands of customers, against attackers ranging from opportunists to state actors.
- Created and executed Google Cloud's multi-year threat detection strategy, aligned with Cloud's goal of being the most secure cloud, and partnered with VPs and GMs on its funding and reporting.
- Scaled detection engineering to planet-wide pipelines running thousands of rules across exabytes of logs.
- Grew the team 5× in three years, hiring across North America and Australia and developing the managers and senior engineers who led the expansion. Managed ~30 people across three continents.
- Ran efficient 24/7, follow-the-sun security investigations.
Featured on the Cloud Security Podcast by Google: Modern Threat Detection at Google (2021).
Mozilla
Head of Security, Firefox Services
2015 – 2020Built and led the security team for Firefox's cloud infrastructure. Reported to the board on Mozilla's security posture, owned product and services security, and set the security roadmap for Firefox's cloud services and release engineering.
- Built a remote DevSecOps team of ~12 from the ground up across North America and Europe, covering security operations, application security, red team and metrics.
- Owned security for 100+ cloud services serving 300M+ Firefox users across AWS, GCP and datacenters.
- Executed a multi-year strategy to mature security operations, reduce incidents and ship products secure by default.
- Created a metrics program that measured maturity and impact and reported security KPIs to leadership.
- Made security part of how ~300 people across dozens of product teams build software, from design review through testing, audits and end-of-life.
- Led incident response for Firefox infrastructure, co-owned the bug bounty program, and sat on Mozilla's security council.
- Built the services behind it: Firefox's code-signing backend (Autograph), secrets management (SOPS), TLS auditing (TLS Observatory) and fraud detection. This work became the book Securing DevOps.
Security Engineer
2013 – 2015- Created MIG (Mozilla InvestiGator) and ran it across thousands of servers, letting investigators query 1,000 endpoints in about ten seconds.
- Co-designed Mozilla's Rapid Risk Assessment framework, adopted across the organization to evaluate product and service risk.
- Wrote Mozilla's Server Side TLS guidelines, a reference used well beyond Mozilla.
- Led application security reviews for web services and APIs, and helped operations teams design secure platforms on AWS.
Earlier career
AWeber · Systems & Security Engineer
2011 – 2013Designed the security of an email marketing platform's web stack and led the redesign of its edge network.
Greenlink Networks · Cloud Engineer
2011Moved a startup's 30+ websites and Oracle database to AWS.
Axians · Security Consultant
2008 – 2010eBanking security and disaster recovery for Société Générale, La Banque Postale and ALD International.
University of Maryland · Research Engineer
2007Built Honeybrid, a honeypot redirection proxy, for my Master's thesis.
MAAF Assurances, Microgate, URSSAF
2002 – 2006Security internship, systems administration and helpdesk.
Education & languages
Master, Information Security Management · University of Poitiers, France
Summa cum laude. Thesis research at the University of Maryland.
Bachelor, Telecommunications Security · University of Tours, France
BTS Informatique de Gestion · ISCB Tours, France
Systems and network administration. Work-study program, half in class and half at URSSAF.
French · native · English · bilingual
Complete index of work
Everything I've written, built and presented, newest first.
Book
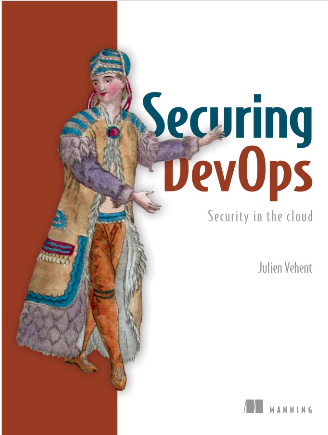
Securing DevOps: Security in the Cloud
Manning Publications, 2018 · 384 pages · ISBN 9781617294136
How to apply DevOps techniques and security together to make cloud services safer. It covers test-driven security in CI/CD, securing web applications and infrastructure, logging and fraud detection, incident response, and risk assessment. Written for operators and security engineers who keep customer data safe.
Essays from jvehent.org
- Ethics, AI and Detection & Response
- Is Living Off The Land the New Zero-Day?
- Probabilities and low signal-to-noise in threat detection
- The experience of the analyst in an AI-powered present
- Are security and reliability fundamentally incompatible?
- Important trends in cybersecurity
- Data Driven Detection Engineering
- How not to use regular expressions
- Managing Remotely
- 7 years at Mozilla
- Beyond The Security Team
- The cost of micro-services complexity
- Interviewing tips for junior engineers
- Maybe don't throw away your VPNs just yet…
Articles & guides
- ReferenceMozilla Server Side TLS guidelinesMozilla's reference guide to TLS protocols, known issues and vulnerabilities, configuration examples and testing tools.
- DevOps : nuageux, avec chance de sécurité · MISC 88 (FR)Security techniques in DevOps, seen through a fictional French startup.
- Mozilla InvestiGator : quand vos serveurs se prennent pour Sherlock Holmes · MISC HS 11 (FR)MIG through three short stories of security investigations.
- A state of the art of SSL/TLS server side · MISC 72The security of SSL/TLS, choosing ciphers and certificates, and the state of transport security.
- Postfix Postscreen: The Zombie Exterminator · GNU/Linux Magazine #147A tour of Postscreen, the zombie blocker in Postfix 2.8. It led to the Postscreen-Stats log parser.
- Web Development with Perl and Mojolicious · GNU/Linux Magazine #138An introduction to Mojolicious through building a URL shortener.
- Fighting Spam with DSPAM · GNU/Linux Magazine #132Filtering spam with DSPAM, a statistical content filter.
- QoS and Traffic Control in the Linux Kernel · GNU/Linux Magazine #127The Linux QoS layer: shaping algorithms, writing a QoS policy, and graphing it with RRDtool and Perl.
- DKIM Email Signature and Verification with DKIMProxy · GNU/Linux Magazine #125The DKIM protocol, DKIMProxy, and deploying DKIM with Debian, Postfix and BIND 9.
Conference talks & workshops
- Protecting Firefox Data with Content Signature · Enigma
- Modern Web Application Security · BSides Tampa, FL
- Test Driven Security in the DevOps Pipeline · AppSecUSA, Orlando, FL
- Securing Your Websites · DevFest Florida, Orlando, FL
- Test Driven Security in Continuous Integration · Enigma, San Francisco, CA
- Continuous Security in the DevOps World · RMLLSec, Paris · slides
- Mozilla InvestiGator: Investigate 1,000 endpoints in 10s · OSDFCon, Washington, DC · slides
- Investigate 1,000 endpoints in 10s with Mozilla InvestiGator · RMLLSec, Paris
- Mozilla InvestiGator: Distributed and Real-Time Digital Forensics at the Speed of the Cloud · BSides Tampa, FL
- Mozilla InvestiGator: Distributed and Real-Time Digital Forensics at the Speed of the Cloud · USENIX LISA15, Washington, DC · SANS DFIR Summit, Austin, TX · HITB, Amsterdam
- SSL/TLS for the Pragmatic · Bucks County DevOps, New Hope, PA
- AFW: Firewalling Dynamic Infrastructures with Chef and Netfilter · Netfilter Workshop / Open Source Days, Copenhagen
- QoS & Traffic Control in the Linux Kernel · Philadelphia Linux User Group · slides
Podcasts
- 2021Modern Threat Detection at Google · Cloud Security Podcast by Google
- 2020Securing DevOps: Security in the Cloud · TestGuild
- —Practical advice for securing the cloud · Teleport, Access Control podcast
- —Securing DevOps in the Cloud · Cloudskills.fm, episode 070
- 2018Securing DevOps · AppSec Podcast
- 2017Épisode hors-série sur DevOps · NoLimitSecu (FR)
Open source on GitHub
- SOPS23k+ stars
A secrets manager that lets teams encrypt, provision and decrypt YAML and JSON configuration files with cloud KMS services. Created at Mozilla; now a community project.
- MIGarchived
Mozilla InvestiGator: distributed, real-time forensics. Agents on every host let investigators inspect file systems, network state, memory and configuration across a fleet in parallel.
Mozilla's digital signature service, which signs Firefox, add-ons, web extensions and internal apps. Signers ship as separate packages: Renard, Margo and PKCS7.
- TLS Observatoryarchived
An observatory for TLS configurations and X.509 certificates, with supporting tools such as cipherscan.
The companion application for Securing DevOps, used throughout the book to build a secure delivery pipeline.
Advanced Firewall: a Chef cookbook that builds host firewall policies for dynamic infrastructure with Netfilter.
An intelligent network proxy that redirects connections from low- to high-interaction honeypots. Master's thesis work at the University of Maryland, also on SourceForge.
A Python log analyzer for Postfix Postscreen.
- Userplexarchived
Propagated users from Mozilla's Person API to downstream systems.
Early career in detail
AWeber · Systems & Security Engineer
Designed and implemented the security of the web stack of AWeber, an email marketing service for small businesses worldwide.
- Wrote security and web architecture provisioning for Opscode Chef in Ruby: AFW, OSSEC, Keymaster.
- Designed highly available web infrastructure with HAProxy, Nginx and Varnish.
- Lead architect for the redesign of the OSPF/BGP/VPN edge network. Replaced aging Cisco routers with 10 Gbps Linux routers (Quagga, OpenVPN, Keepalived, Conntrackd).
- Deployed and maintained OSSEC host intrusion detection, and built geolocation algorithms in Python to detect suspicious activity.
- Ran internal and external penetration tests, taught internal security and automation classes, and served on the level-2 on-call rotation.
Greenlink Networks · Cloud Engineer
Rebuilt the hosting infrastructure for a startup's 30+ rewards-program websites. This is where I first adopted AWS, back in 2011.
- Turned a single-node Java platform into a load-balanced cluster.
- Migrated all components to AWS, including the Java websites and the Oracle database.
- Ran 24/7 operations as the on-call sysadmin, DBA, QA and sometimes developer.
Axians · Security Consultant
Information and web security for banks and financial institutions in the Paris area.
- La Banque Postale (2010), web security engineer, architecture team: eBanking access control, system and network partitioning, J2EE security (SSL/TLS, IBM IHS, WAS 6, MQ, web services cryptography), security assessments and risk analysis.
- ALD International (2009), IT security engineer: business continuity methodology and IT disaster recovery for 40+ locations and two datacenters. Designed recovery architectures and ran continuity tests.
- Société Générale (2008), web security engineer, eBanking architecture: front-end security and performance, applied cryptography, SSL/TLS on J2EE, WebLogic and HAProxy, Qualys audits and firewall rules.
University of Maryland · Research Engineer
Center for Risk and Reliability, in Dr. Michel Cukier's team.
- Built Honeybrid, a TCP/UDP proxy in C on Linux 2.6 that redirects connections from low- to high-interaction honeypots, using a B-tree based decision engine.
- Studied network attacks against Linux and Windows systems in honeypot environments.
MAAF Assurances · Intern to the Chief Security Officer
- Built Perl tooling for security log processing and antivirus monitoring, and worked on the information system's compliance with French privacy law.
Microgate · Systems Administrator
- Migrated email infrastructure to Linux, Postfix and Cyrus with an OpenSSL PKI and OpenLDAP directory, and designed site-to-site links with OpenVPN.
URSSAF · Part-time Helpdesk
- Helpdesk and administration of Windows NT/2000 networks for the French social security funding agency in Tours, as part of a work-study program.